OPEN TO SOC ANALYST LEVEL 1 OPPORTUNITIES
LOVE
HINGU
Love Hingu — Cyber Security and SOC Analyst L1 Candidate
Cyber Security / SOC Analyst L1 Candidate

I build practical security projects focused on security visibility, alert monitoring, and cyber security engineering.

01 NETWORK SECURITY Traffic analysis & defense foundations
02 SIEM & WAZUH Telemetry aggregation & rules
03 EDR / XDR Endpoint correlation & host audit
04 GANPAT UNIVERSITY B.Sc. IT — Cyber Security
01 ABOUT LOVE HINGU

Curious by nature.
Methodical by habit.

I am a Cyber Security enthusiast focused on practical security monitoring, network security, and security engineering projects.

My interest lies where monitoring, investigation, and network security meet. I'm especially engaged with SIEM tooling, Wazuh, and EDR/XDR concepts — building practical projects to develop hands-on understanding of security operations.

ACADEMIC FOUNDATION

B.Sc. IT — Cyber Security

Graduation in progress at Ganpat University

CAREER OBJECTIVE

SOC Analyst Level 1

Open to SOC Analyst Level 1 opportunities

02 PRACTICAL SECURITY WORK

Built to make
security visible.

Three applied projects spanning security operations dashboarding, surveillance intelligence, and predictive analytics. Click any image or button to inspect screenshots.

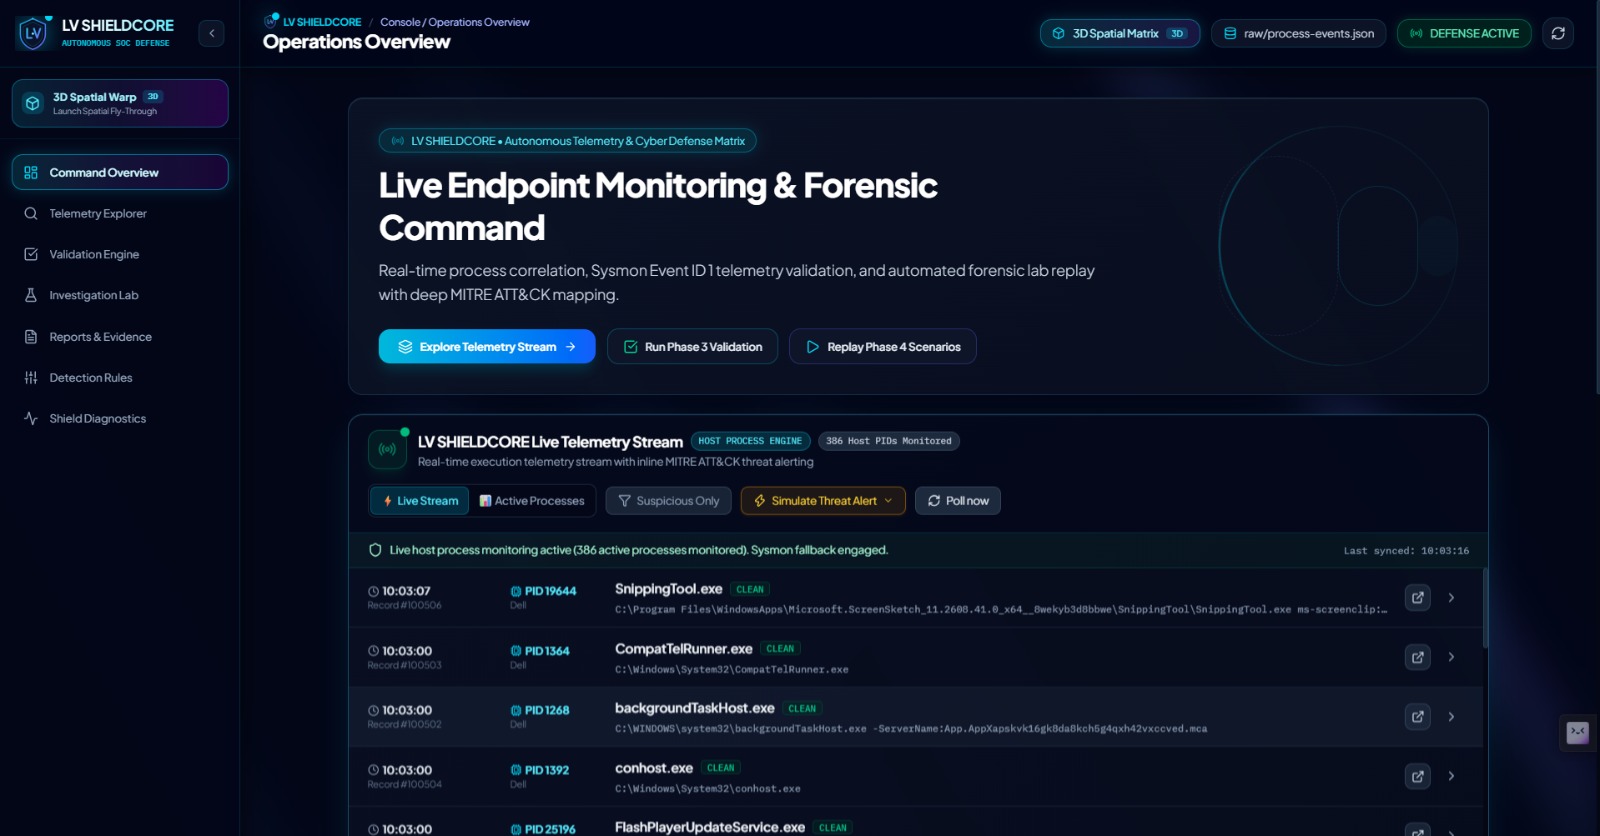
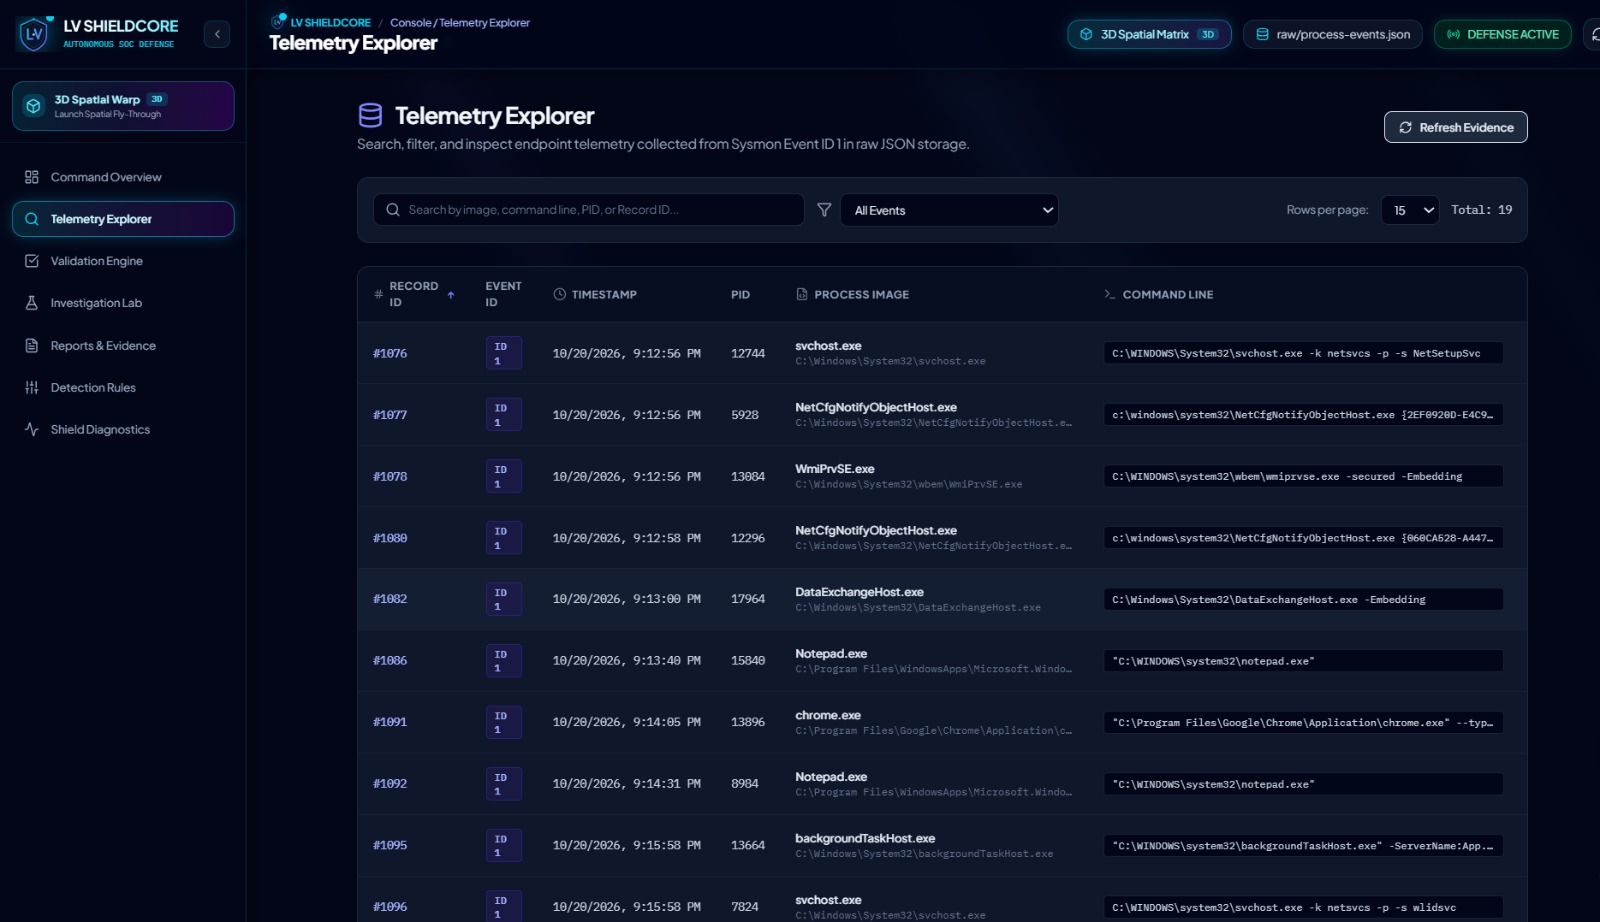
LVShieldCore Operations Overview — live endpoint monitoring and telemetry stream LVShieldCore Telemetry Explorer — Sysmon Event ID 1 telemetry data table
● VERIFIED WORKING BUILD
PROJECT 01 SIEM DASHBOARD WORKING BUILD

LVShieldCore

A SIEM-style security dashboard designed for endpoint monitoring and forensic visibility. The current working build includes an operations overview with live telemetry stream, a telemetry explorer for searching and filtering Sysmon Event ID 1 data, and an alert monitoring view.

Operations Overview Dashboard
Alert Monitoring & Event Filtering
Sysmon Event ID 1 Telemetry Explorer
SIEM Endpoint Telemetry Sysmon Event ID 1 Alert Monitoring
Request Walkthrough
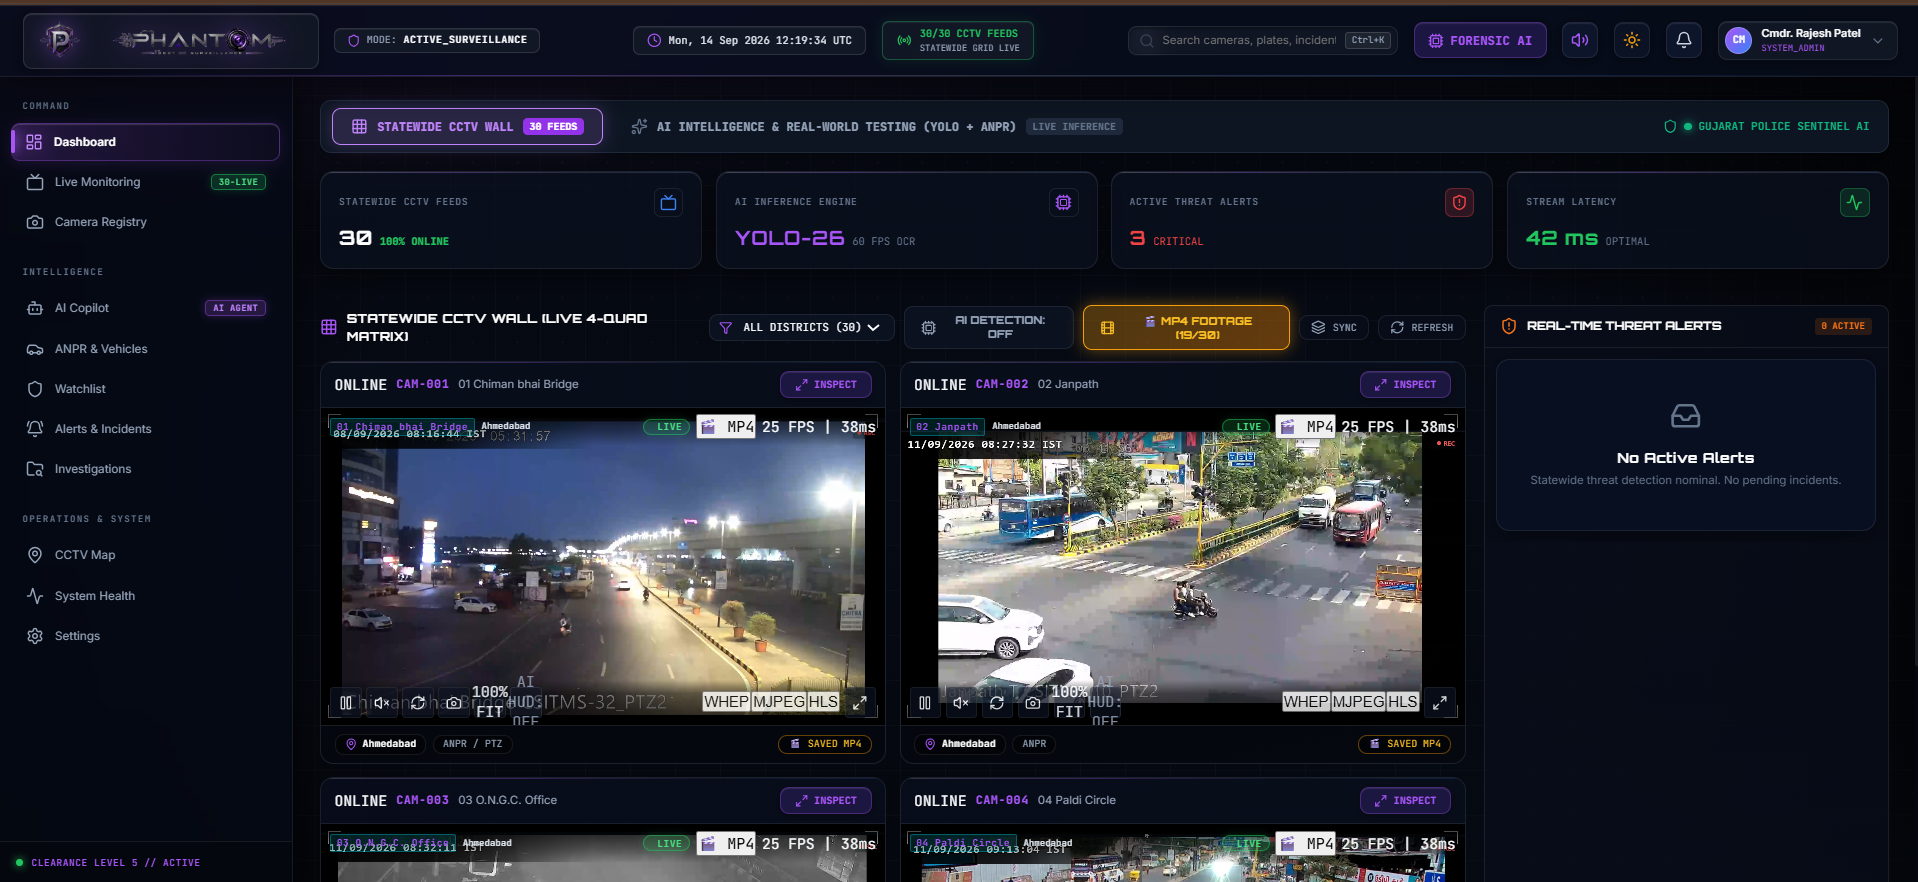
PHANTOM:360 statewide CCTV monitoring matrix with AI inference engine
PROJECT 02 HACKATHON PROJECT

PHANTOM:360

A CCTV surveillance and video intelligence hackathon project developed for the Gujarat Police Hackathon. The system demonstrates a statewide camera monitoring matrix with live video feeds, AI inference integration using YOLOv8 for automated detection, ANPR capabilities, and a dedicated commander access portal.

Surveillance Intelligence YOLOv8 CCTV Matrix ANPR
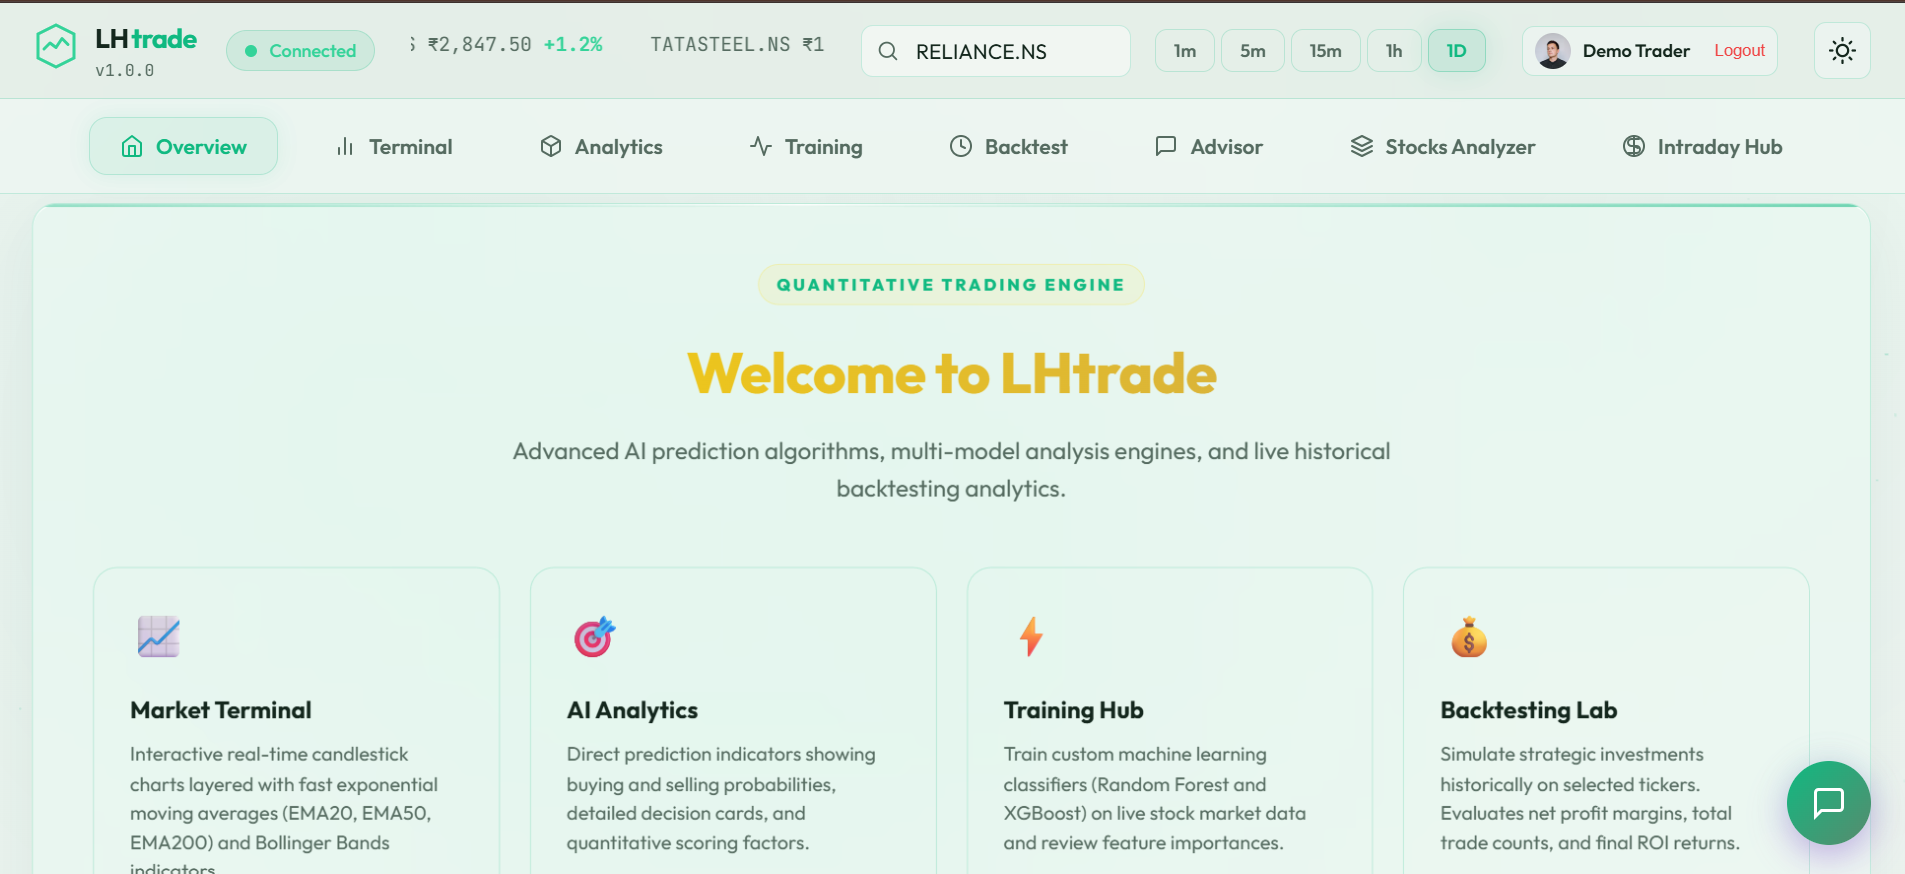
LVTrade quantitative market prediction engine and backtesting platform
PROJECT 03 EARLY PROJECT

LVTrade

A stock market prediction and quantitative analysis platform representing the starting point of my project-building journey. Features an interactive market terminal with candlestick charts, AI decision analytics with indicators, a machine learning training hub utilizing Random Forest and XGBoost classifiers, and historical backtesting simulation.

ML Modeling Quantitative Analytics Random Forest XGBoost
03 TECHNICAL FOCUS AREAS

Applied skills &
core interests.

Stated technical interests and practical competencies developed through coursework, lab environments, and project engineering.

01

Network
Security

Building foundational understanding of network architecture, protocol analysis, traffic packet inspection, port auditing, and perimeter defense strategies.

02

Security
Monitoring

Focusing on alert triage visibility, log aggregation, event correlation, false-positive reduction, and standard SOC Level 1 operational workflows.

03

SIEM &
Wazuh

Hands-on practical exploration of Security Information and Event Management, specifically Wazuh agent deployments, rule configuration, and centralized event indexing.

04

EDR &
XDR

Studying host-level telemetry, process creation trees, Sysmon logging, and cross-layered extended detection mechanisms across modern security stacks.

04 PROFESSIONAL DIRECTION

Targeted career path:
SOC Analyst L1

I am actively seeking SOC Analyst Level 1 roles where I can contribute to real-time incident monitoring, alert triage, log investigation, and practical defense operations.

Open to SOC Analyst Level 1 opportunities

Ready to bring disciplined attention to 24/7 security operations, ticket triage, and alert verification.

Applied SIEM & Log Investigation

Continuously building practical lab experience with Sysmon telemetry, Wazuh, and event correlation.

Graduation in progress at Ganpat University

Enrolled in B.Sc. IT with specialized curriculum in Cyber Security and network infrastructure.

05 INITIATE CONTACT

Have an opportunity
worth securing?

For SOC Analyst Level 1 opportunities, technical interviews, or project discussions, I welcome professional inquiries.